160+ guardrails,
six families.
Guardrails apply across the hierarchy — lower levels can tighten thresholds, but they can never weaken locked rules.

Safety
Toxicity blocking, bias detection, and harmful-content filtering on agent output.

Quality
Hallucination thresholds and faithfulness and coherence checks, enforced before delivery.

Compliance
Policy enforcement logging with locked rules for critical alerts, reviewable by compliance officers.
160+
GUARDRAILS

Privacy
PII detection and masking — social security numbers, card data, personal data, custom patterns.

Security
Prompt-injection defense and jailbreak prevention, scored on every interaction.
Cost
Budget caps, token-explosion detection, and waste alerts at every level of the hierarchy.
Your data never leaves your boundary
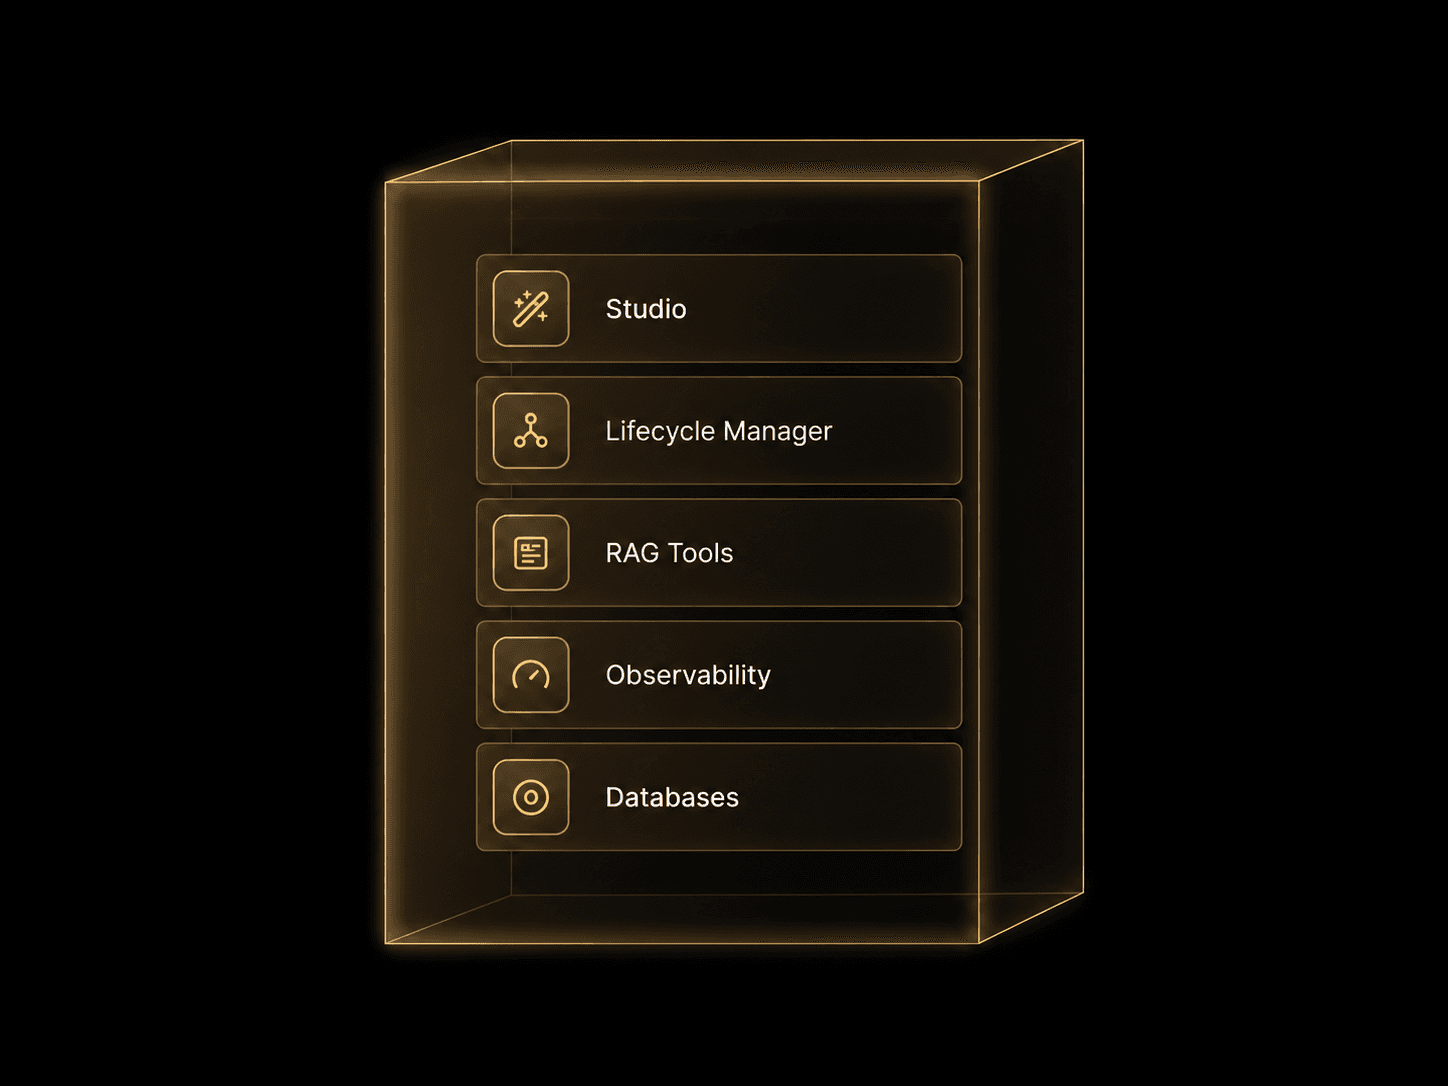
Every service — studio, lifecycle manager, RAG, tools, observability, databases — runs inside your Kubernetes cluster, in your VPC, in your subscription. PHTN.ai has zero access to your production environment. The only traffic that leaves your boundary is the LLM call itself, and only if you choose a hosted model. Sensitive data is protected at seven enforcement points, from document upload through retrieval, model context, agent output, alerts, and audit logs.
A hardened software supply chain

01
Static Analysis (SAST)
Source, bytecode, and binaries scanned in the CI/CD pipeline for injection flaws, hardcoded secrets, and more.

02
Dynamic Testing (DAST)
Real-world attack simulation against live platform instances.

03
Composition Analysis (SCA)
Every third-party and open-source component scanned for known CVEs and supply-chain risk.

04
API & Auth Testing
OpenAPI-based security testing on all endpoints, plus authorization testing across every RBAC permission.

05
Red-Team & Pentest
Regular penetration tests, plus adversarial testing for prompt injection and jailbreaks. Reports under NDA.

06
Runtime Defense
Real-time monitoring through the AIOps pipeline, anomaly detection, and a kill switch when confidence drops.
Evidence, not assurances
Security evidence packages — penetration test reports, per-image SBOM, red-team results, remediation history, incident-response procedures, and an exportable role-permission matrix — are provided to your cybersecurity team under NDA.
Platform controls align to SOC 2, HIPAA, GDPR, and PCI-DSS requirements, with compliance-officer and read-only auditor roles built into the platform's access model.
Security Evidence
 Penetration test reports
- SBOM per image
- Red-team results
- Remediation history
- Incident response procedures
- Role-permission matrix