01
Retrieve
Read-only Access
- Scoped identity + access
- Usage logging
- Baseline quality
HOME | insights | OFFICIAL POV
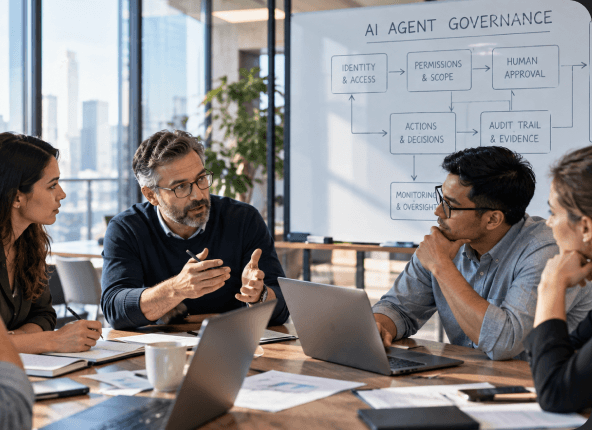
Regulated enterprises govern AI agents by controlling delegated authority, not by adding another policy layer around the model. Before an agent can act inside a regulated workflow, the enterprise needs to know whose authority it is using, which systems and data it may access, what decisions it may make, what requires human approval, what evidence is retained and who owns the outcome.
In May 2026, Gartner argued that agent governance should scale with autonomy and access. NIST’s 2026 work on software-agent identity likewise highlights identification, authorization, auditing and non-repudiation as core concerns when agents gain access to enterprise systems. [1][2]
The operating question is therefore not simply whether an agent is accurate. It is whether material actions can be bounded, observed, reconstructed and contained, with accountability remaining clear when the system acts at machine speed.
Photon Point of View
“Govern the authority before the agent gets access.”
Delegated Authority
The control boundary should follow authority, not the model label.
01
Read-only Access
02
Propose: Human Executes
03
Write After Explicit Approval
04
Act Independently Inside Bounds
MORE AUTHORITY • STRONGER RUNTIME CONTROL
Figure 1
Control intensity should rise with delegated authority and write access.
02
Regulation matters because it changes what an enterprise has to prove when an AI-enabled process is challenged. The exact obligations depend on jurisdiction, sector, the organization’s role, and the classification and use of the system. The architecture should make those differences mappable rather than hard-coded into separate governance stacks.
In Europe, the AI Act became broadly applicable on August 2, 2026, and Article 50 transparency requirements also began applying on that date. Following the AI Omnibus, rules for high-risk systems in Annex III apply from December 2, 2027, while rules for high-risk AI embedded in regulated products apply from August 2, 2028. Not every AI agent is a high-risk system; enterprises need to classify the actual system, role and use case before determining which obligations apply. [4][5][6]
For EU financial entities, DORA has applied since January 17, 2025 and harmonizes requirements around ICT risk management, incident reporting, resilience testing and third-party ICT risk. For an AI-enabled workflow that depends on models, APIs, cloud platforms and external data providers, the practical implication is to understand the full operational dependency chain around the agent, not simply the model itself. [7]
The UK continues to operate through a regulator-led, sector-specific model rather than an EU-style horizontal AI act. In January 2026, the UK government asked 19 regulators, including the FCA, PRA and ICO, to publish plans for enabling safe AI-powered innovation within their existing remits. [8]
In the United States, AI obligations remain distributed across federal requirements, existing sector and consumer-protection authorities, and a growing body of state legislation. NCSL maintains a database of introduced and enacted AI measures across states and territories. [9]
The practical implication is not to build a separate governance architecture for every rulebook. It is to establish a common evidence layer that can repeatedly answer the questions regulators, risk teams and internal audit ask: What acted? Under whose authority? What data and tools were used? Which approval or rule applied? What changed? Can the action be contained or reversed? Which third parties were involved?
One evidence spine
Do not create a separate governance architecture for every jurisdiction.
Role + Risk
ICT Resilience
Sector Rule
Federal + State
Who initiated?
Which agent?
What could it do?
What did it use?
What gate applied?
What changed?
Who owns it?
RUNTIME CONTROL LAYER
monitor • evaluate • escalate • contain • retain evidence
Figure 2
One evidence spine maps many rulebooks to a reusable chain of authority, action and outcome.
03
A governance platform can enforce policies, observe activity and generate evidence. It cannot decide which business decisions an enterprise should delegate to an agent. That decision belongs in the operating model.
Before tooling is selected, the enterprise needs to define the business outcome, risk boundary, accountable owner, agent decision rights, permitted data, escalation conditions and the point at which the agent must stop. HFS Research has found that accountability and decision rights remain fragmented in many enterprise AI operating models, which makes the operating model a prerequisite rather than a downstream governance task. [10]
Photon’s AI Governance Advisory establishes the governance strategy: ownership, decision rights, policy, risk classification, approval thresholds, evidence requirements and escalation paths. PHTN.ai operationalizes the portions that need runtime enforcement across agents, models, clouds and business lines. Tooling should implement an agreed governance model; it should not become the place where the enterprise discovers what its governance model is. [11]
Photon’s Business and Human Value framework adds another discipline: delegated authority should create enough business and human value to justify the control, operating cost and risk being introduced. [12]
04
For one regulated financial-services enterprise, a multi-system compliance workflow deployed in production reduced manual processing time by 70–90% while maintaining full audit integrity. Every agent decision generated a tamper-evident record, creating an evidence trail that could be reconstructed without returning the workflow to manual control.
The significance is not simply the efficiency gain. The workflow automated more of the underlying activity without removing the evidence needed for oversight. That is the standard regulated enterprises should apply to agentic AI: greater autonomy should not come at the expense of accountability.
05
The process is examined first. The value baseline is agreed. Architecture, governance and ownership are designed together. A bounded workflow is placed into production. The team observes failure modes, quality, cost, adoption and human intervention, then expands only when the operating evidence supports it.
For a bounded workflow with accessible data and integration paths, Photon teams can target roughly 6–10 weeks from process audit to a first production deployment. This is a Photon delivery target, not a universal market benchmark or commitment. Complex integrations, data remediation, regulated approvals, procurement dependencies or substantial process redesign can extend the path.
The principle matters more than the calendar: production readiness should be designed from the first engagement, not added after the pilot is declared successful.
Photon’s AI Engineering practice builds and operates production systems, while Client Outcomes makes the evidence explicit. The objective is not to scale every pilot. It is to move the right workflows into production with process, governance, ownership and value already designed around them.
Explore Photon’s AI Engineering approach, or contact Photon to discuss the path from pilot to production.
Four questions before scale
The test is not how many pilots have succeeded. An enterprise is ready to scale when the next use case can inherit foundations created by the previous one.
What authority are we delegating, and who remains accountable for the outcome?
Can we reconstruct every material action well enough for risk, audit or regulatory review?
Can we prove where sensitive data travels across the agent
Can we constrain, stop and recover the agent when behavior, cost or risk exceeds the approved boundary?
Figure 3
Four production-governance questions to answer before expanding agent autonomy.
Primary and supporting sources used to validate this POV.
Accessed October 1, 2026.
Agent governance should scale with autonomy and access.
Identification, authorization, auditing and non-repudiation for software agents.
Agent governance as a core AI investment.
Horizontal EU framework for AI systems.
Updated application dates for high-risk AI rules.
Transparency obligations that began applying on August 2, 2026.
ICT risk, incident reporting, resilience testing and third-party risk.
Regulator-led plans for safe AI-powered innovation.
Introduced and enacted AI measures across states and territories.
Accountability and decision rights remain fragmented in many AI operating models.
Photon governance strategy: ownership, decision rights, policy and evidence.
Photon BHV framework.